HackTheBox — Puppet"
Password reuse was the key. One reused password led to mailbox access, then to the app creds hidden in email.
Password reuse was the key. One reused password led to mailbox access, then to the app creds hidden in email.
The real path is **password reuse** across the email accounts + a web-app exploit. So the next move is: reuse The `password` on the other mailboxes and read email to find internal app creds.
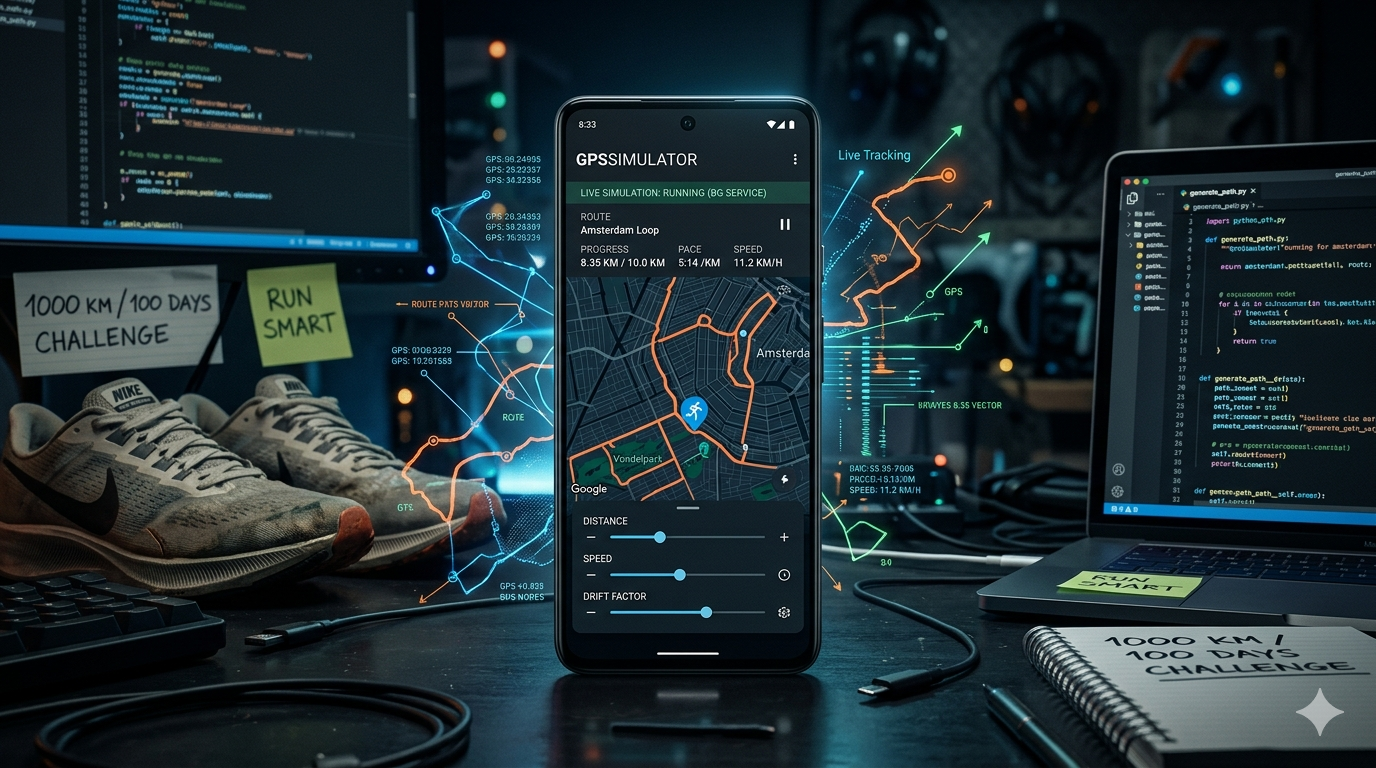
Raw GPS spoofing is easy. Making it look like a real person ran that route is the hard part. GPSSimulator tackles that problem through realistic route shaping, natural pace variation, and a clean setup flow that makes simulation repeatable without friction.
A collection of cybersecurity CTF challenges created for University CTF 2026, featuring Web, Cryptography, and Forensics categories with realistic scenarios, Dockerized setups, and beginner-to-hard level challenges for learning and competition.
A Hack The Box Principal write-up covering web discovery, token abuse, credential reuse, and privilege escalation to root.
A TryHackMe Active Directory write-up covering LDAP enumeration, Kerberoasting, SMB abuse, and domain compromise.
A TryHackMe write-up covering HopAI web enumeration, DNS zone transfer abuse, mail workflow abuse, and model prompt extraction.
A detailed walkthrough of the CTF challenge, covering reconnaissance, enumeration, exploitation, and privilege escalation.
A TryHackMe Hoppers Origins write-up covering chatbot command injection, internal service enumeration, and multi-host privilege escalation across the lab.
A TryHackMe Side Quest 2 write-up covering enumeration, GDB-assisted key recovery, payload storage abuse, and hidden service discovery to gain foothold access.